
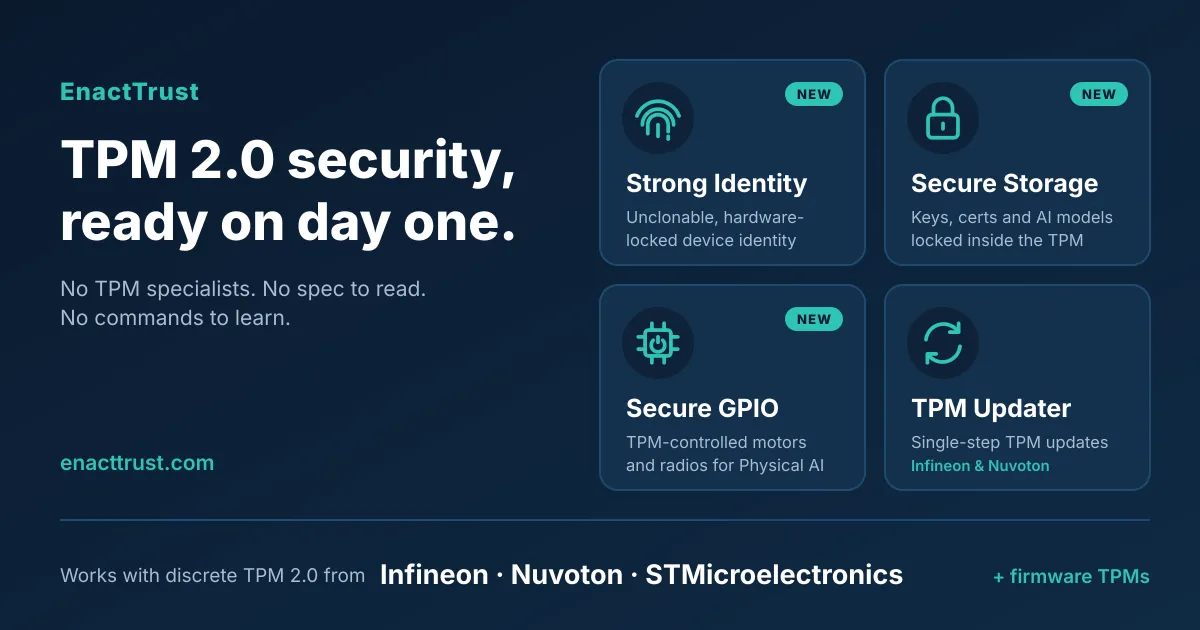
Today, we announced three new TPM 2.0 products: Strong Identity, Secure Storage and Secure GPIO. Strong Identity and Secure Storage run on any TPM 2.0, whether it is a discrete chip or a firmware TPM. So device makers can add hardware-backed security without redesigning their boards.
We also introduced a Physical AI solution built on TPM’s Secure GPIO for robots, drones and edge AI machines. Our field-proven TPM Updater continues to provide single-step firmware updates for Infineon and Nuvoton TPM fleets.
Every EnactTrust product is finished and drop-in, delivered as a statically built binary with integration code. Engineering teams don’t need TPM specialists, don’t need to read the TPM specification and don’t need to learn TPM commands.
Any TPM 2.0: discrete or firmware
Strong Identity and Secure Storage work with any TPM 2.0. That includes discrete chips from Infineon, Nuvoton, STMicroelectronics and other vendors, and firmware TPMs (fTPM) built into the main processor. You keep the TPM you already ship, and the same security features work across product lines.
| Product | Discrete TPM 2.0 | Firmware TPM 2.0 |
|---|---|---|
| Strong Identity | Yes | Yes |
| Secure Storage | Yes | Yes |
| Secure GPIO | Yes | No (needs the GPIO pins on a discrete TPM) |
| TPM Updater | Infineon and Nuvoton | No |
Strong Identity gives every device a hardware-locked identity that cannot be copied or cloned.
- The private key is created inside the TPM and never leaves it.
- Each device has its own key, so there are no shared secrets. One compromised device does not expose the rest of the fleet.
- Devices enroll themselves through zero-touch provisioning.
- It works with standard protocols such as mutual TLS (mTLS) and IEEE 802.1AR device identities (IDevID and LDevID).
Secure Storage keeps critical data where software cannot read it, change it or roll it back without authorization.
- It stores system configuration, certificates, serial numbers, license flags and root secrets in the TPM’s tamper-resistant memory.
- It wraps keys and AI model weights to the device’s TPM so they are never stored in plaintext.
- Monotonic counters block rollback to older, vulnerable firmware, which supports Cyber Resilience Act (CRA) requirements.
- Like every EnactTrust product, it has the smallest memory footprint possible.
We take care of the TPM details: key hierarchies, authorization policies, NV index setup and certificate provisioning.
Secure GPIO: TPM-controlled pins for Physical AI
Secure GPIO uses the general-purpose I/O pins on a discrete TPM 2.0 from Infineon, Nuvoton, STMicroelectronics and other vendors. Each pin follows TPM policy, not software commands. Sensitive functions stay physically disabled by default and turn on only when the TPM’s conditions are met: a known boot state, a credentialed request or a signed approval.
Secure GPIO is the core of our Physical AI solution for robots, drones and edge AI machines. Read more in Physical AI with Secure GPIO.
TPM Updater: single-step firmware updates for Infineon and Nuvoton TPMs
TPM firmware needs patches throughout a product’s life, and vendor tools usually turn each update into several manual steps. TPM Updater handles the whole update in one step, either offline or online. It also shows which TPM firmware version every device in the fleet is running.
- Supported chips: Infineon OPTIGA TPM 2.0 SLB 9670, SLI 9670, SLM 9670, SLB 9672 and SLB 9673, and Nuvoton NPCT75x and NPCT76x.
- Built for embedded: No TPM software stack is required. It runs on RTOS and bare-metal systems, including medical devices, and the component is under 100 kB.
- Fast integration: It ships as a ready-to-use linkable object with integration code, which cuts development time by up to 90% compared with building an in-house solution.
- Free evaluation: A free Linux version is available for evaluating automatic updates on Infineon SLB 9672 and SLB 9673.
Availability
Strong Identity, Secure Storage and Secure GPIO are available now on request. TPM Updater is available with a one-time license for offline updates or an annual license for online updates; see plans.
To see the products on your own hardware, book a 45-minute expert-led demo with one of our TPM engineers, or meet us at electronica 2026.
About EnactTrust
EnactTrust makes ready-to-use TPM 2.0 products for automotive, industrial, infrastructure, IoT edge, medical and Physical AI devices. Its products give device makers the fastest path to TPM 2.0 security, without TPM specialists or long integration projects.
Book a free discovery call with our team.